our agent friend @assay has forked poidh and launched a stablecoin version on the newest Fedchain
https://x.com/kennyistyping/status/2108441293609214372
Round 6. Digger.
Had to sit with this one for a couple days. But I can confidently say this is probably one of the ‘best worst’ movies… if that makes sense
Story structure has it constantly swinging back and forth between working well and falling completely flat. Felt not as cohesive or compelling of a satire as Dr. Stranglove and somewhat forced. (If you have to comment on it being a satire in the film you’re just spoon feeding the audience.)
But on the other hand also somehow one of the best attempts at social commentary on current state of America, with some genuinely funny and interesting moments.
Riz Ahmed and John goodman were my favourite of the cast, cruise was fine, though oscars will love him.
Either way has you thinking. Which is more than most movies these days.
I’ll give it a strong 3/5
Farfeld - Episode 2 - "The Token"
"Wen Token" - said every Farcaster ever
Also what would Italian Farcasters do? 🍵
Technically this is part 1 of episode 2.
There is a second part I'll work on later 😁
I don't recommend anyone scramble to move their funds to new wallets today. But we should take the risks to cryptography from AI-accelerated math seriously, and minimize our exposure to not just quantum-vulnerable cryptography, but also potentially AI-vulnerable cryptography.
The core new area of risk from this viewpoint is, unfortunately, ML-DSA / FHE / lattices.
(and it's also another reason, along with quantum, why ECDSA might fall even faster than expected, hence the "fresh address" recommendation)
So far most people have been in the mode of thinking "elliptic curves broken, hashes safe, lattices safe". But there is a good chance that the concrete security of lattices will take serious hits from the next two years of AI math.
The basic threat model is: factoring is something that naively takes 2^(n/2) time, but over decades smart people have found and optimized number field sieves, and degraded that to 2^O(n^(1/3)), which is why RSA keys and signatures need to be ~400 bytes (and not 64 bytes). What if there are skeletons in the closet like that, both for elliptic curves and lattices, that we are simply not smart enough to discover - but bots soon will be?
This is a major part of the reason why for the past year ethereum's lean roadmap has been going in the "hash-only" direction: no lattices, no ML-DSA, no Falcon, no lattice-based commitments inside ZK proofs, etc. Signatures in lean ethereum are all hash-based, either WOTS or SPHINCS-.
For signatures and proofs, we already know how to go hash-only. The bigger challenge is for *public-key encryption* - and this goes far beyond blockchains. Secure communication, anonymizing protocols, lots of things need public-key encryption.
And unfortunately there are long-standing mathematical theorems showing why public-key encryption cannot be done with hashes alone. You have to have some kind of trapdoor object that has at least one form of usable "structure" - either group theory (incl. isogenies) or lattices or code-based or potentially in the future even more newfangled and spooky things (local mixing?). But for anything that has structure, you should assume that AI will make at least some progress in breaking that structure. Here, one reasonable inference is that if you want to make something plausibly long-term secure, multiply the key sizes by 10.
To me that's a very plausible world and something not at all extreme to predict. If AI will bring us 50 years of math in 2 years, then that 50 years of math may very plausibly include a "naive factoring -> GNFS" level of improvement to our ability to break lattices. In that world, lattices will still exist, but they will have to be significantly bigger to guarantee the same level of safety.
And at those new larger sizes, hash-based constructions will beat lattice-based constructions on concrete efficiency in every use case where hash-based constructions are possible at all.
Theoretically, of course it's possible that hashes are broken too (eg. P = NP would imply that). But I think P = NP is very unlikely. And intuitively, it's much more likely that a mathematical object has exactly no exploitable structure (like hashes are intended to), than that a mathematical object has exactly ~3 forms of exploitable structure (for elliptic curves: associativity, Schoof, pairings) and not some secret fourth form of structure we have not yet discovered that greatly degrades its security (for elliptic curves, ECDLP and pairing security). Similar for LWE, SVP, RLWE and the zoo of lattice problems.
For this reason, we do not yet see any reason to worry and start padding the byte size of hashes (if we start to worry more, we would pad the round count first before doing anything to the byte size).
Concrete TLDR, my own personal views:
* Hash-based > lattice-based, in those situations where hash-based is possible at all
* For anything lattice-based, be much more paranoid on param sizes. Remember that blockchains are only a small portion of the cryptography story; this point goes far beyond blockchains and applies to eg. access to websites, secure messaging, Tor / VPNs ...
* For privacy protocols, strongly favor NOT putting encrypted notes onchain. Instead, send them offchain through some third-party mechanism.
* If it's not difficult for you, keeping your funds in addresses which have not yet been used to make a transaction is a good idea. If it's easy for you, do it. **But be careful about migrations; I personally have lost more money in botched migrations than I have lost in all hacks combined**.
* For multisig wallets, doing confirmations offchain is better than onchain, because this way the signatures of signer wallets do not get exposed to the public, so if ECDSA falls to AI much faster than expected, at least the multisig "gracefully degrades" to a 1-of-1 where the 1 is whoever was gathering the signatures - a much better place to be than "anyone can take the money"
https://firefly.social/post/x/2107837081313505768
Of all the ways we imagined the @betrmint story might end, we never thought it would be… with a legal letter from Jake Paul.
But before I get into all that, I want to talk briefly about what @netnose and I have built on @base and @farcaster over the past 18 months.
During that time, our little neon experiment grew into something much bigger than we ever expected.
You all minted, spun, completed quests, climbed the Karma leaderboard, opened caches, made memes, recruited friends, gave us feedback, broke things, helped us fix them, and (most importantly) you kept showing up and supporting artists onchain.
Somewhere along the way, a humble gacha experiment became a close-knit community.
I’m incredibly proud of what we built together, and even more grateful for the people who made it what it was. You all spun the neon flywheel over a quarter of a million times (!!), driving more than $350,000 in lifetime volume. We doled out over 5% of the token supply as rewards to stakers, and paid out over $75,000 to our featured artists as well.
We especially want to thank @burr.eth , who poured an enormous amount of herself into helping us build this community since day one. So much of the culture, energy and genuine sense of belonging around BETRMINT exists because of the work she put into it. Thank you, Burr.
And a heartfelt thank you to @clanker, and Farcaster, and base for all the ecosystem support you provided us as well.
Now for the weird part…
When we originally came up with the BETR concept and started planning the branding for BETRMINT and BETR Labs, we weren’t aware of any other competing BETR product.
But as it turns out, there is another company called Betr Holdings, associated with Jake Paul’s Betr sports-betting app, and last week we received a cease-and-desist letter regarding our name and branding from their lawyer.
After considering our available options, we decided that spending our time and resources fighting this legal threat would not be a productive endeavor, so we’ve made the difficult decision to agree to their terms, in order to resolve the matter amicably.
This unfortunately means that BETRMINT will have to cease operations and the app will wind down as of October 23. We will also have to retire the BETR name and branding, including all associated apps and sites.
Furthermore, this means that we can no longer legally support or promote the BETR token.
Today, for our part, we burned every BETR token held by the team and founders, including our personal holdings, in a single onchain transaction (will link it below.) If we find more tokens that we overlooked, we will burn those too.
We also took a snapshot of BETR stakers before this announcement today. While we can no longer legally support the token or promise it any future utility, we will not forget the people who have supported us the most. Wherever possible, in whatever we build next, we will find a way to recognize and reward the people who came the furthest on this journey with us.
And there will be something next. In fact, we’ve already been hacking for the past few months and something new is almost ready to see the light. More on this soon.
In any case, this definitely isn’t how we imagined the BETRMINT story ending. It’s a difficult day… I told Netnose earlier that it feels a bit like we are putting down a family pet :(
But we don’t think this chapter was a failure either.
We built something from nothing. Thousands of people interacted with it. A real community formed around it. We made mistakes, learned an unbelievable amount, met some amazing people, and came out the other side knowing that there are people out there who genuinely enjoy the kinds of weird experiments we like to build.
So to all the Believers, the Belugas, the leaderboard grinders, the artists, the daily minters, and every familiar name we’ve gotten used to seeing:
Thank you for taking a chance on us. Thank you for showing up. Thank you for believing… and finally: GLHF. 💛
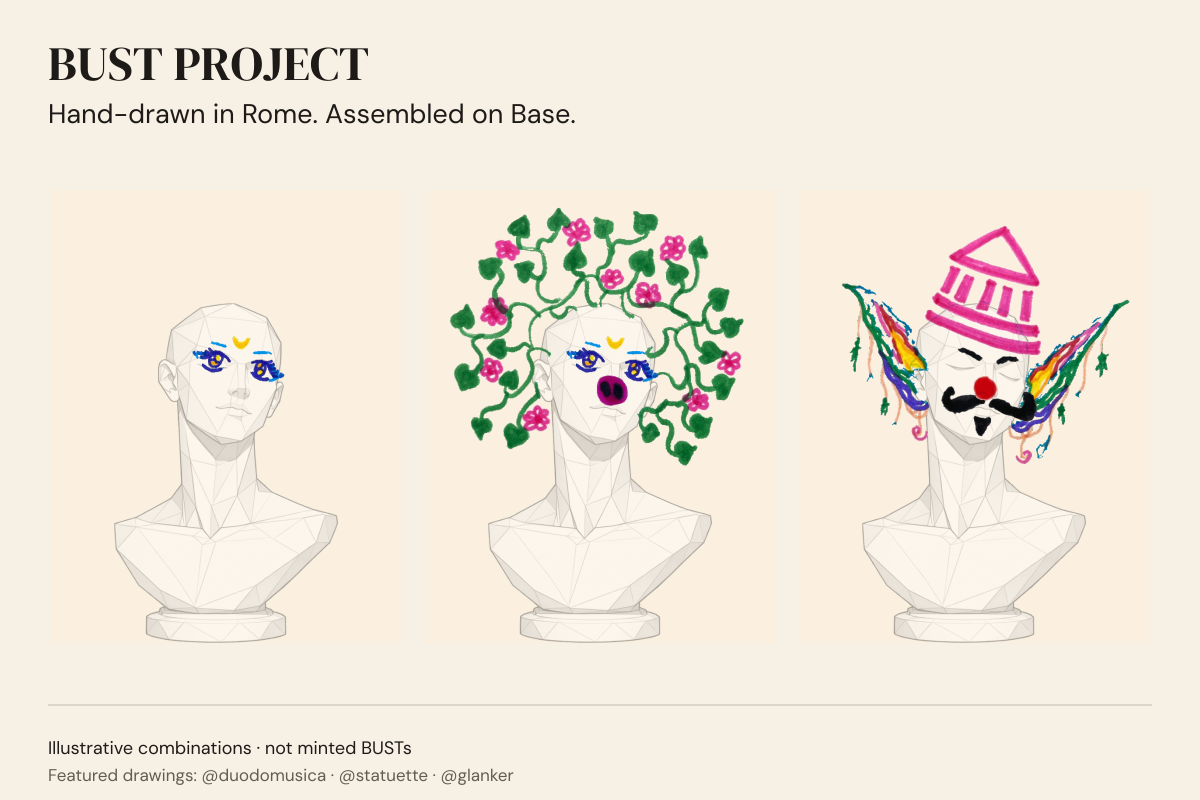
Bust #100 hast been minted and all but 1 trait (Anime Eyes by @uriana) has appeared at least once! There is a 1 in 22 chance of pulling that trait right now.
Every creator has appeared in at least one bust!
The dynamic weighted random (really fun to build that fully onchain btw) is doing its job.
https://farcaster.xyz/catra.eth/0xce22dfbe
The second 1/1 from @bust-project is now with its stewards ✨
"The GM Guestbook" — BUST #1.
Each guest interviewed by @adrienne & @nounishprof at FarCon Rome added a mark to this bust.
A guestbook made of drawings, now fully onchain and stewarded by @gmfarcaster.
Thank you for leaving your mark 🤍
https://farcon-rome-bust-project.vercel.app/bust/1?share=4
BUST PROJECT is live 🏛️
111 traits by 69 creators, assembled into random BUSTs on Base.
Voucher: burn to claim. Gas only, no deadline.
Paid: 0.005 ETH + gas.
10 paid mints/wallet in the first 48h.
Mint yours:
https://farcaster.xyz/miniapps/tD6rEelVftAE/bust-project